










Hong Kong business · Product selection and integration

ZenarmorProducts and features

Apply software protection at gateways, endpoints and cloud environments, centrally managing internet policies, application traffic and private-network access.

Manufacturer information reviewed: 2026-10-13

Partner listed in the vendor directory

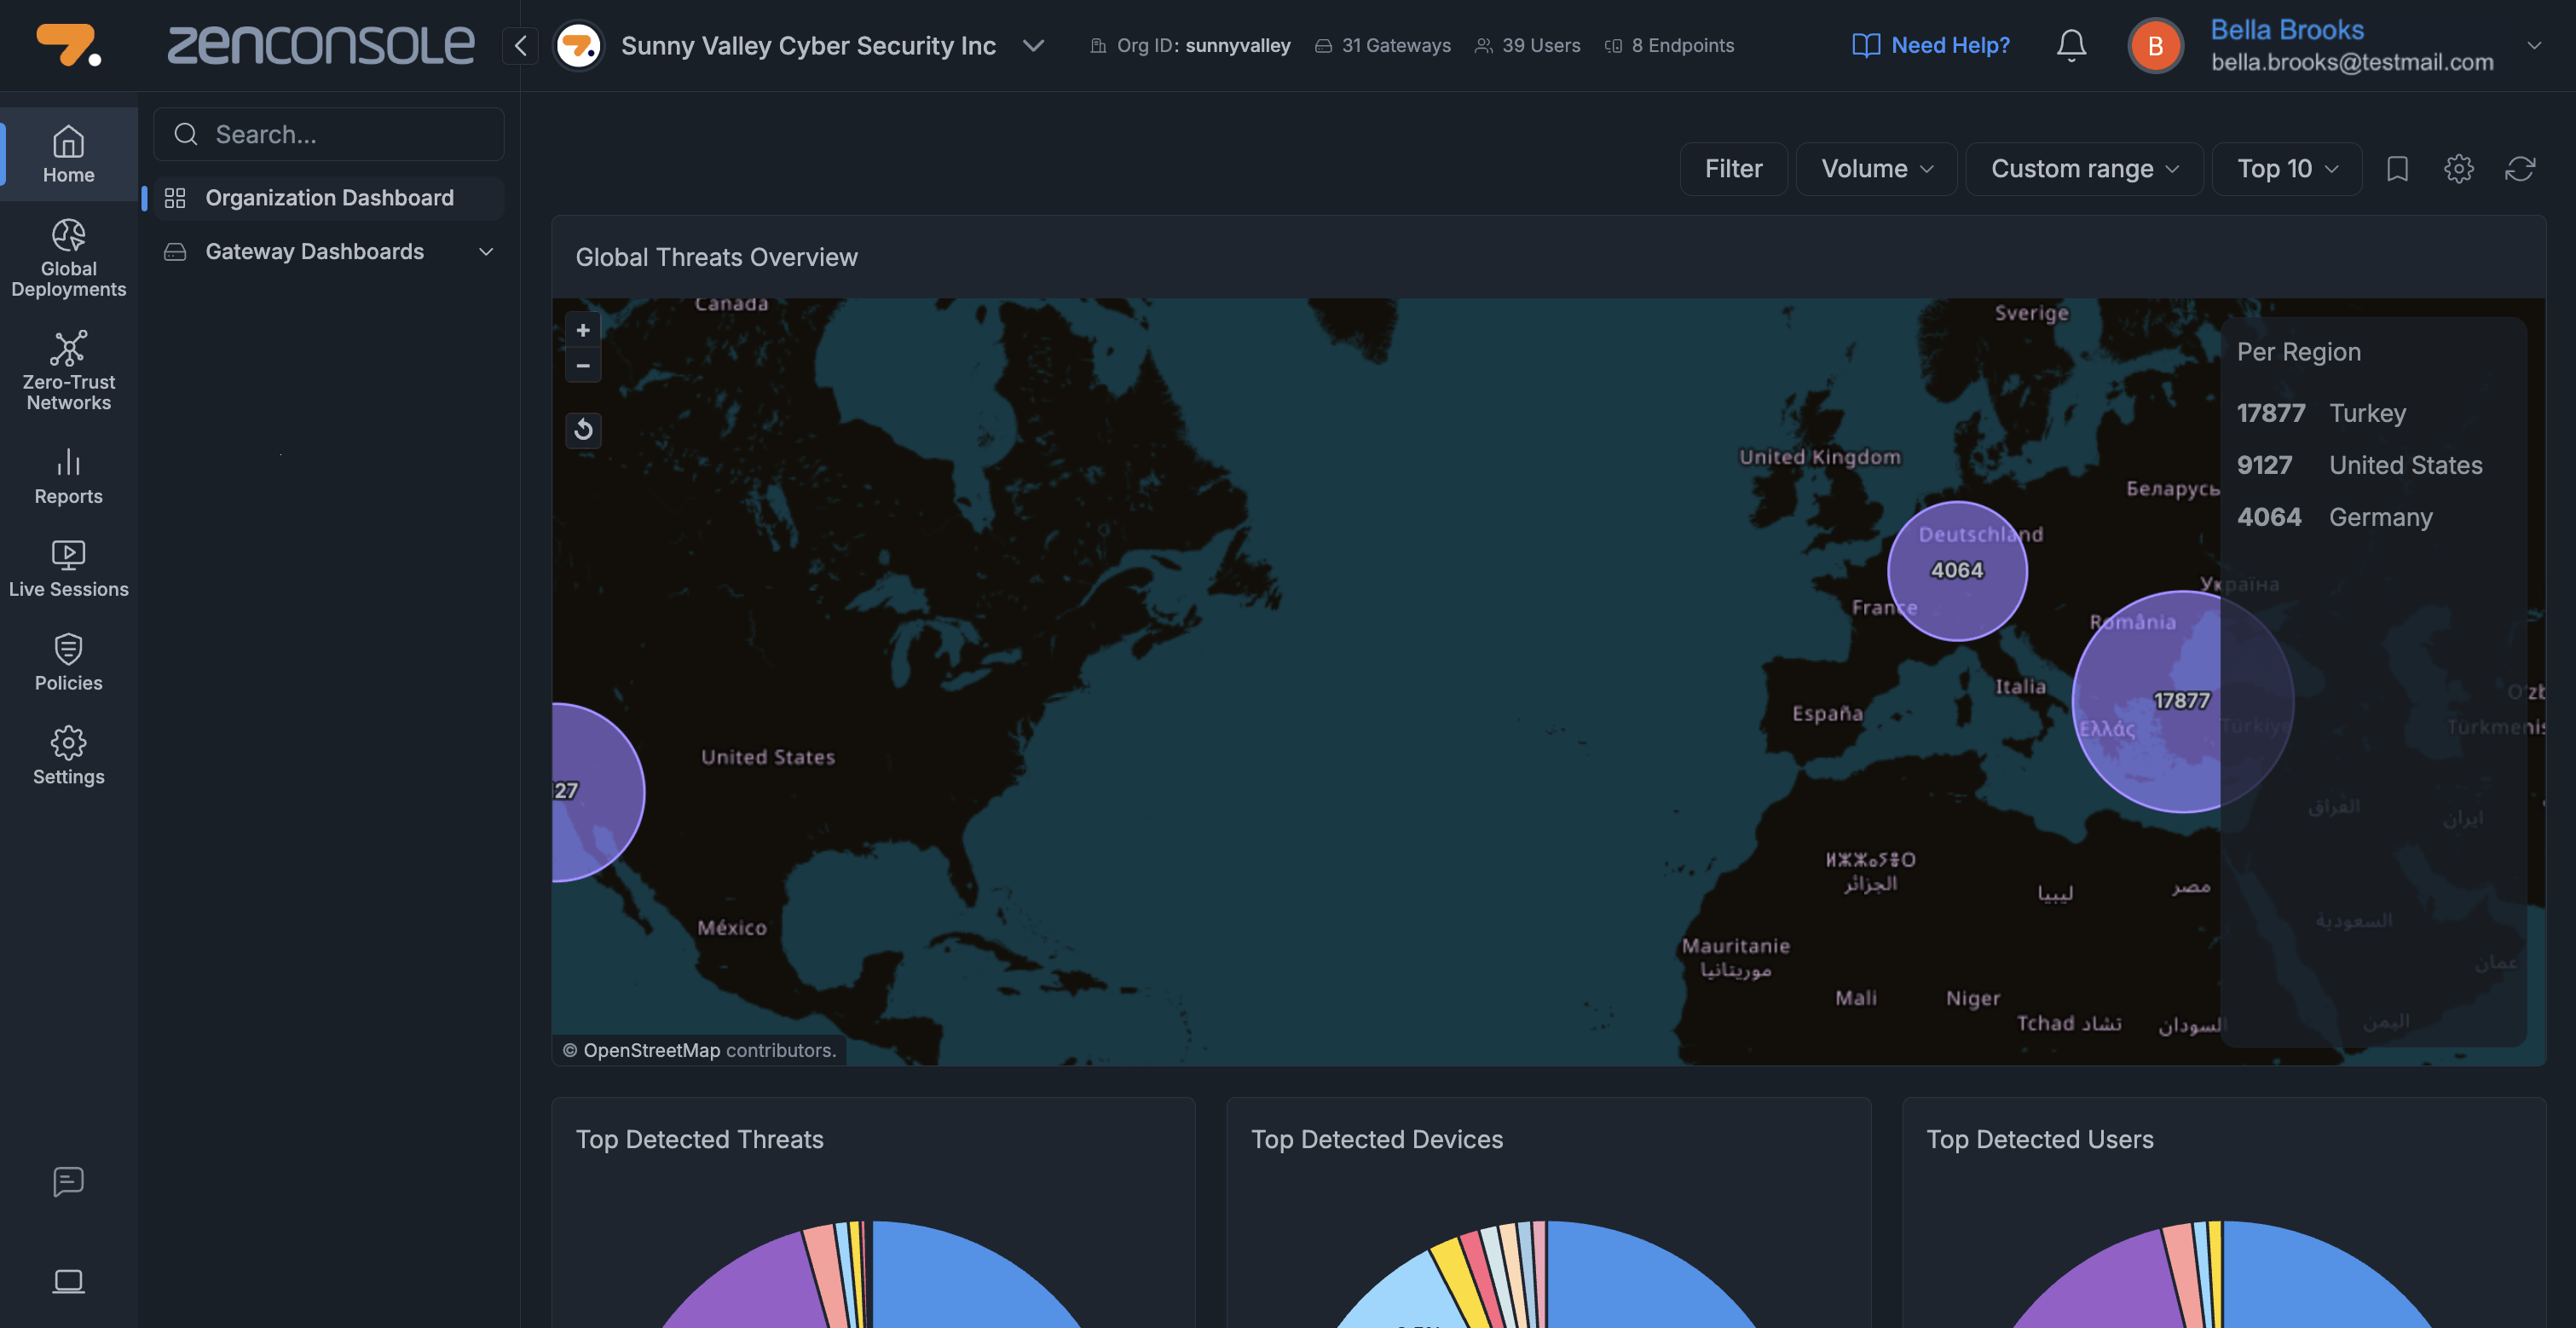
Official Zenarmor Zenconsole organisation dashboard and threat-distribution interface
Vendor Zenconsole organisation dashboard example, using vendor sample data.Vendor image source
5Product and feature categories
5Manufacturer resources
Manufacturer documents and technical information

PRODUCTS & CAPABILITIES

Product capabilities and environments

Covers Unified Secure, Unified Secure Plus and enterprise SSE / ZTNA / SASE. Legacy NGFW Business subscriptions remain supported with entitlements different from new plans.

Unified Secure | Business gateway protection

Provide NGFW / SWG policies and central management for offices and branches.

  • Unify web and application access policies
  • Combine IPS and DNS traffic inspection
  • Manage gateways and security reports centrally

Suitable scenariosOffice and branch gateways

Key capabilities and scope
  • Network and web filtering with application control
  • IPS and deep DNS inspection
  • Cloud IdP and captive-portal authentication
  • Gateway HA and central reporting

Suitable environments
Office gateways · Business branches · Local networks

Full TLS decryption is an add-on entitlement. Confirm user, agent and site quotas by plan. Local AD integration in legacy Business NGFW does not automatically carry over.

Enquire about product solutions

Unified Secure Plus | Mobile and multi-site protection

Extend gateway protection to remote users and private-network connections.

  • Extend protection through mobile-device agents
  • Includes full TLS inspection entitlement
  • Connect users and sites within quotas

Suitable scenariosHybrid workplaces and multi-site organisations

Key capabilities and scope
  • Endpoint agents and full TLS inspection
  • Mesh VPN and site connections
  • Overlay networks with redundancy and failover
  • Private-network analytics

Suitable environments
Hybrid work · Multi-site businesses · Remote endpoints

Plans limit agents, sites, overlay networks and report retention. TLS inspection requires a trusted CA and appropriate exclusions.

Enquire about product solutions

SSE | Secure internet access

Extend web, application and encrypted-traffic policies across workplaces.

  • Extend web policies across work locations
  • Inspect encrypted traffic and DNS risks
  • Manage SaaS and data flows according to plan

Suitable scenariosRemote staff and corporate SaaS access

Key capabilities and scope
  • SWG web filtering
  • Full TLS inspection
  • CASB and data loss prevention controls
  • DNS threat protection and central management

Suitable environments
Remote employees · SaaS access · Gateways and endpoints

TLS decryption requires endpoint trust certificates and privacy/compatibility assessment. Confirm CASB/DLP scope, deployment and licensing by plan.

Enquire about product solutions

ZTNA | Private-resource access

Authorise connections to private business applications and networks using identity and device posture.

  • Authorise by identity and device posture
  • Access private resources through encrypted connections
  • Limit access scope with microsegmentation

Suitable scenariosInternal applications and remote private access

Key capabilities and scope
  • Encrypted peer-to-peer connections
  • Policies based on identity, device and resource
  • Microsegmentation and continuous policy evaluation
  • Integration with specified EDR device-posture signals

Suitable environments
Internal applications · Remote access · Branches and private networks

Confirm EDR/identity integrations and agent/gateway requirements. Continuous access evaluation needs valid signals and correctly configured policies.

Enquire about product solutions

SASE | Unified network and access policies

Combine internet protection, private access and network policies in one platform.

  • Combine web protection and private access
  • Unify identity, policies and traffic analysis
  • Manage multi-location deployments centrally

Suitable scenariosCross-region, hybrid-work and cloud environments

Key capabilities and scope
  • SSE, ZTNA and network protection together
  • Identity / SSO and organisation policies
  • Gateway, endpoint and cloud deployments
  • Multi-tenant console and traffic analytics

Suitable environments
Hybrid-work businesses · Cross-region networks · Multiple sites and cloud environments

SASE combines security capabilities. Confirm modules, licences and compatible platforms against the selected business or enterprise plan.

Enquire about product solutions

VENDOR RESOURCES · AL-TOUCH SELECTION NOTES

Technical resources and deployment essentials

Review features, deployment requirements and selection notes, then consult complete vendor documentation as needed.

Manufacturer guide

Zenconsole deployment introduction

Review initial endpoint and gateway setup, organisation enrolment and connectivity for central management.

  • Plan endpoint and gateway deployment separately
  • Connect managed devices using organisation identifiers
  • Verify service and management connectivity after installation

Publicly readable

Read vendor resource
Manufacturer guide

TLS encrypted-traffic inspection guide

Plan endpoint trust certificates, TLS policies and application exceptions, understanding prerequisites for HTTPS inspection.

  • Endpoints must trust the inspection CA certificate
  • Create dedicated TLS policies by interface
  • Handle application exceptions such as certificate pinning

Publicly readable

Read vendor resource
Manufacturer eBook

ZTNA remote-access ebook

Explore zero-trust access and Zenarmor deployment around remote work and distributed teams.

  • Access scenarios for remote and distributed teams
  • Limitations of traditional access methods
  • Zenarmor's ZTNA design approach

Available after vendor registration

Read vendor resource
More vendor resources 4 items
Manufacturer guideSASE quick-start guideManufacturer platform capabilities and initial deployment workflow.Manufacturer guideQuick installation and gateway deployment guide2026 deployment and Zenconsole guidance.Manufacturer guideFull TLS inspection deployment guideTrusted CA, endpoint configuration and inspection requirements.Manufacturer guideZenarmor SASE / ZTNA eBookManufacturer eBook entry point; some resources require registration.

Need to assess compatibility with existing systems?Discuss compatibility, deployment and licensing with the team.

Enquire about products and deployment

From product selection to deployment and maintenance

Describe your systems, scale and improvement needs to plan configurations, licences and deployment with the team.

Contact our Hong Kong team Local services and deployment →Browse other brands →