Hong Kong business · Product selection and integration

WebRAY cybersecurityProducts and features

Protect business websites, APIs and AI applications, following up risks through scanning, asset inventories and log analysis.

Manufacturer information reviewed: 2026-10-13

Channel cooperation and security product services

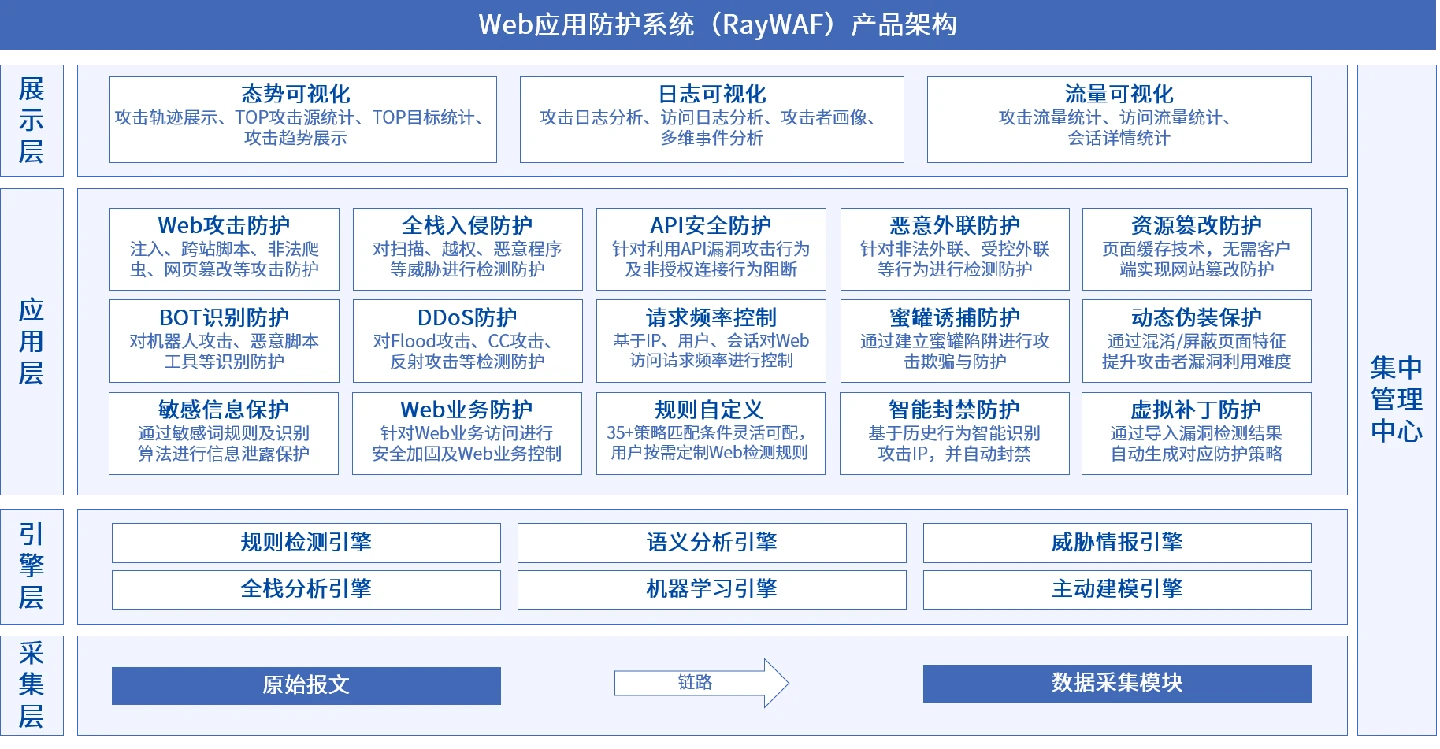
Official WebRAY RayWAF architecture showing collection, detection engines, web/API protection and visualisation layers
Official RayWAF product architectureVendor image source
6Product and feature categories
4Manufacturer resources
Manufacturer documents and technical information

PRODUCTS & CAPABILITIES

Product capabilities and environments

Six product families cover websites, APIs, vulnerabilities, assets, AI gateways and logs. Select according to risks, architecture and licences.

RayWAF | Web application protection

Protect business websites and public applications with attack rules, traffic analysis and API protection.

  • Inspect attacks against websites and applications
  • Manage API and bot access risks
  • Select deployment modes for the network architecture

Suitable scenariosBusiness websites, online services and web applications

Key capabilities and scope
  • Web-attack and OWASP Top 10-related protection
  • API identification and request/response inspection
  • Bot, brute-force and abnormal-traffic protection
  • Deployment options including reverse proxy, inline and out-of-band

Suitable environments
Business websites · Online services · Internal web applications

Test WAF policies against applications and manage exceptions. DDoS capability depends on equipment, traffic and upstream scrubbing arrangements.

Enquire about product solutions

RayScan | Vulnerability assessment

Check hosts, websites, databases and configuration risks, producing a list of vulnerabilities to validate and fix.

  • Assess host, website and database risks
  • Organise asset and vulnerability inventories
  • Recommend remediation from scan findings

Suitable scenariosServers, websites and network equipment

Key capabilities and scope
  • Host, web, weak-password, baseline, database and image checks
  • Asset inventories and grouping
  • Vulnerability risk analysis and remediation advice

Suitable environments
Servers · Websites · Databases · Network equipment

Authorise scan scope and intensity and agree maintenance windows beforehand. Results still require validation and remediation.

Enquire about product solutions

RayAPI | API security governance

Identify exposed APIs, permission issues and data-access risks to plan monitoring and protection.

  • Discover API endpoints from traffic
  • Check authentication and abnormal calls
  • Track sensitive data and access records

Suitable scenariosAPI services and mobile application backends

Key capabilities and scope
  • Discover APIs from traffic and catalogue interfaces
  • Check authentication, unauthorised access and abnormal calls
  • Sensitive-data identification and access restrictions
  • Attack-event analysis and access auditing

Suitable environments
API services · Mobile application backends · Business data interfaces

Detection, restriction and masking depend on deployment mode and protocols. Test effects on legitimate operations.

Enquire about product solutions

RayMatrix | Asset and vulnerability governance

Organise assets, vulnerabilities and owners, tracking remediation and retesting.

  • Combine asset and risk data from multiple sources
  • Link assets, vulnerabilities and responsible owners
  • Track remediation, retesting and closure

Suitable scenariosCross-department asset and vulnerability governance

Key capabilities and scope
  • Combine active, passive and third-party data
  • Unified asset maps and attack-surface comparison
  • Asset risk overview
  • Ticket assignment, remediation tracking, retesting and archiving

Suitable environments
IT assets across departments · Cloud and on-premises assets · Vulnerability management workflows

Integration depends on data sources and connectors. Reports inform management; assess Hong Kong regulatory applicability separately.

Enquire about product solutions

RayToken | AI security gateway

Manage access, data and activity between business applications and large-model services.

  • Unified access to public and private models
  • Inspect prompt injection and sensitive data
  • Record model calls and usage

Suitable scenariosEnterprise AI applications and model interfaces

Key capabilities and scope
  • Unified access to public and private models
  • Prompt-injection and content-safety checks
  • Sensitive-data loss prevention for inputs and outputs
  • Tiered access, API-key management and call auditing

Suitable environments
Enterprise AI applications · Large-model APIs · Internal knowledge and workflows

Confirm model support, SaaS or private deployment and data flows individually. Guardrails do not replace model evaluation and human governance.

Enquire about product solutions

RayLAS | Log auditing and management

Centralise equipment and system logs for incident tracing, alert analysis and audits.

  • Collect device and system logs centrally
  • Normalise formats and search events
  • Support correlation analysis and audit reports

Suitable scenariosSecurity-device, host and application logs

Key capabilities and scope
  • Collect logs from different equipment and systems
  • Normalise formats, centralise storage and search keywords
  • Correlate and visualise security events
  • Statistical reports and audit-access management

Suitable environments
Security equipment · Hosts and databases · Network and application logs

Plan log ingestion, capacity, retention and viewing rights. Assess applicable Hong Kong requirements separately.

Enquire about product solutions

PRODUCTS · SERVICES · LOCAL DELIVERY

Bring security capabilities into daily operations

AL-Touch helps clarify requirements, select products, coordinate deployment and follow up on remediation and maintenance. Work involving vendor experts is subject to confirmed regions, personnel, authorisation and scope.

01

Asset discovery and security assessment

Identify exposed websites, systems and significant weaknesses before prioritising remediation.

Vendor products and services
RaySpace asset discovery, RayScan vulnerability assessment and vendor penetration testing within an authorised scope.
How AL-Touch can help
Identify assets and system owners, coordinate authorisation and test windows, explain findings and follow up on retesting.
Deliverables to agree
An asset inventory, prioritised findings, remediation owners and retest records.
Vendor service information ↗
02

Website, API and application protection

Match security policies to real business traffic and reduce the impact of attacks and false blocks.

Vendor products and services
RayWAF web application protection, RayAPI API security and related modules selected for the environment.
How AL-Touch can help
Assess integration, certificates and traffic paths; coordinate deployment, tuning, approved exceptions and rollback.
Deliverables to agree
Deployment diagrams, a policy baseline, acceptance tests and maintenance handover.
Vendor service information ↗
03

Exposure, log and threat monitoring

Track changes to public assets and unusual signals, with clear ownership for follow-up.

Vendor products and services
Exposure and sensitive-information monitoring, RayLAS log management and vendor managed security where contracted.
How AL-Touch can help
Define monitoring sources, data flows, retention, alert priorities, recipients and review arrangements.
Deliverables to agree
Monitoring coverage, an alert-handling workflow and a periodic improvement list.
Vendor service information ↗
04

Incident response and business recovery

Prepare responsibilities for reporting, containment, evidence preservation and restoration.

Vendor products and services
Vendor incident response and compromise assessment, with expert support confirmed for the incident.
How AL-Touch can help
Coordinate the vendor and customer IT team, organise initial incident information, containment and recovery, and follow up on remediation.
Deliverables to agree
Response contacts, an action timeline, recovery validation and recommendations; forensic scope is agreed separately.
Vendor service information ↗
05

Staff awareness and exercise planning

Help staff recognise suspicious messages, protect accounts and report concerns.

Vendor products and services
Vendor phishing simulation within approved participant groups and scenarios.
How AL-Touch can help
Help define participants, communications and privacy arrangements, then turn exercise findings into practical guidance.
Deliverables to agree
An exercise plan, aggregate results, training priorities and follow-up checks.
Vendor service information ↗
06

AI use and data security

Clarify data, permissions and external connections before introducing AI assistants and enterprise knowledge bases.

Vendor products and services
RayToken AI security gateway, with model access, sensitive-data handling, access controls and auditing assessed by edition.
How AL-Touch can help
Compare local and cloud deployment, define approved data and permissions, and organise pilots, usage policies and activity records.
Deliverables to agree
Data-flow diagrams, an AI-use inventory, a permissions matrix and pilot acceptance criteria.
Vendor service information ↗

Agree the scope before engaging specialists

Penetration testing and red-team exercises require written authorisation, agreed targets, test windows and stop conditions. Round-the-clock SOC/MDR, digital forensics, onsite response and compliance audits require separately confirmed teams, service hours, evidence handling and contracts.

Automated monitoring, human analysis and onsite support are specified separately. Product purchases and vendor qualifications do not include every specialist service.

Plan enterprise security services →
VENDOR CREDENTIALS

WebRAY organisational credentials

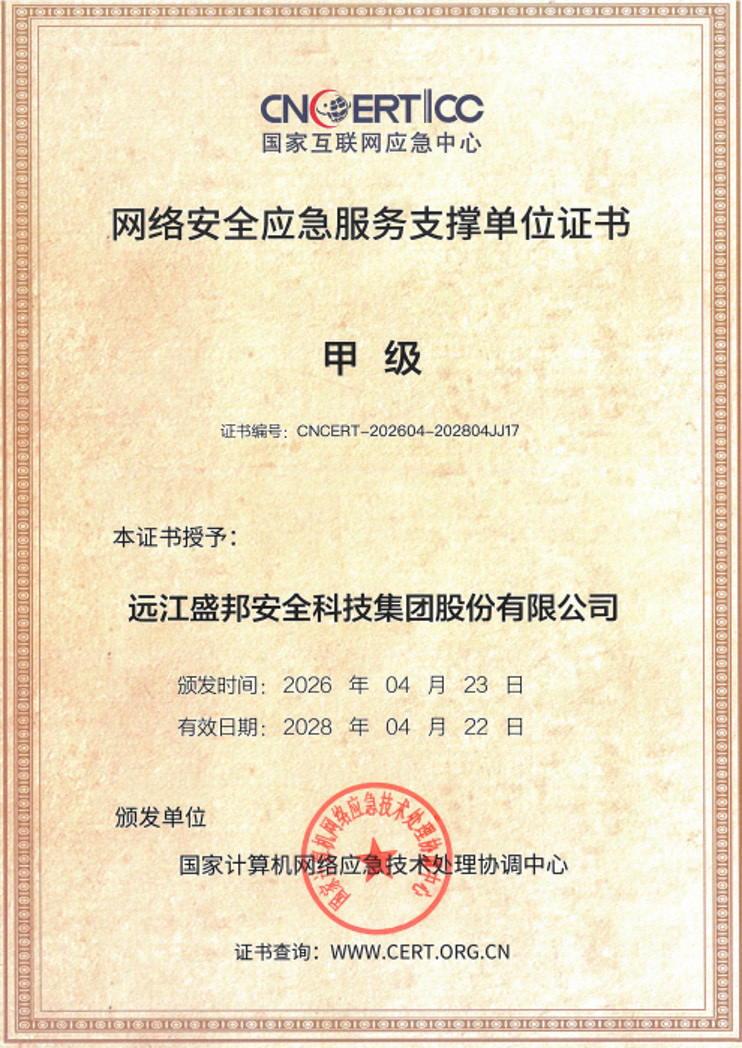
The certificates below are held by 遠江盛邦安全科技集團股份有限公司. AL-Touch coordinates local planning, deployment and project follow-up; vendor credentials are shown against their named holder and scope.

CNCERT cybersecurity emergency service support organisation — Grade A — 遠江盛邦安全科技集團股份有限公司

CNCERT cybersecurity emergency service support organisation — Grade A

Organisational qualification for cybersecurity emergency service support.

Validity stated on certificate2026-04-23 — 2028-04-22

View original certificate image ↗
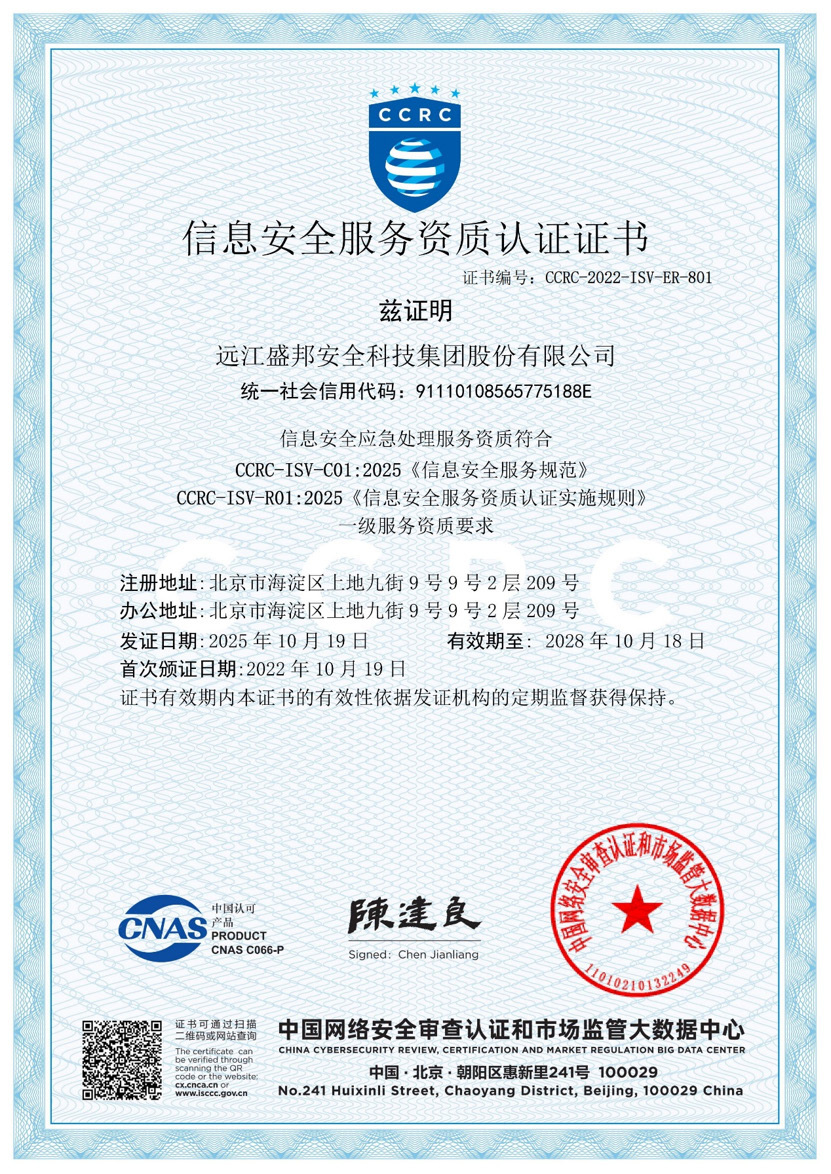
CCRC security incident response — Level 1 — 遠江盛邦安全科技集團股份有限公司

CCRC security incident response — Level 1

Information security incident response service qualification.

Validity stated on certificate2025-10-19 — 2028-10-18

View original certificate image ↗
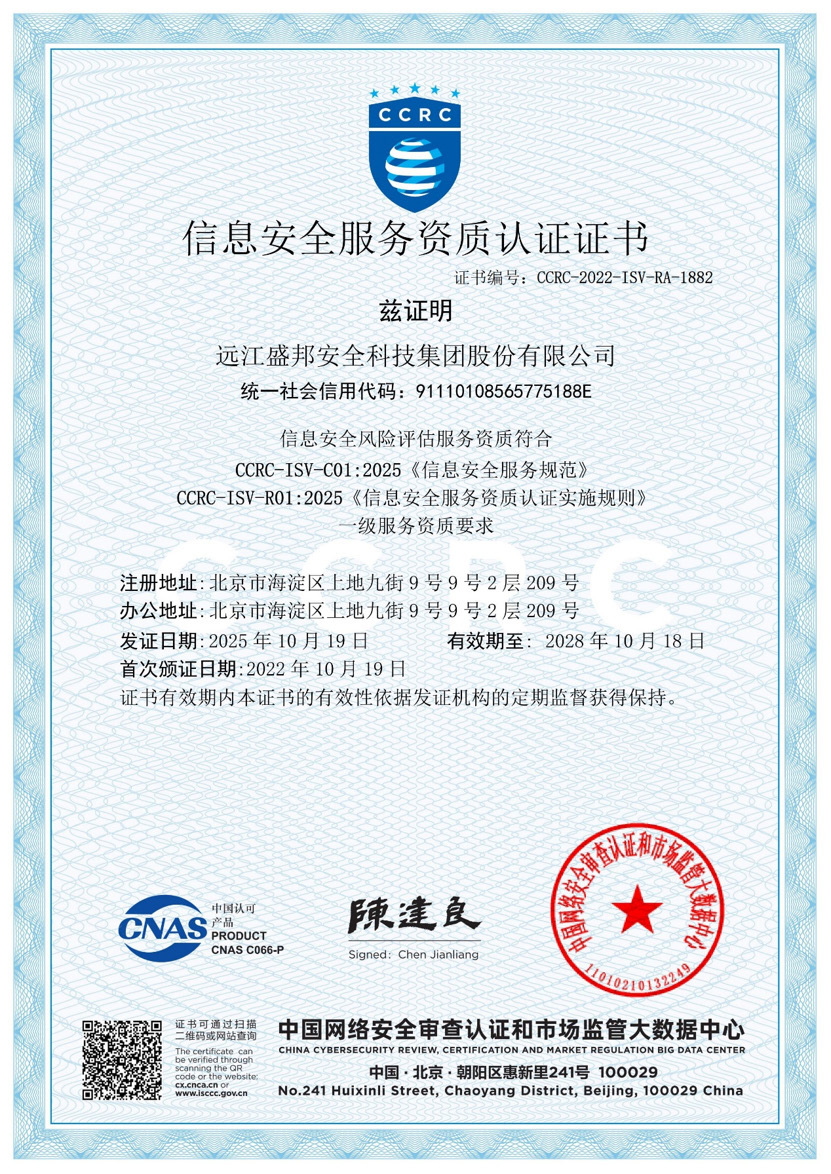
CCRC risk assessment — Level 1 — 遠江盛邦安全科技集團股份有限公司

CCRC risk assessment — Level 1

Information security risk assessment service qualification.

Validity stated on certificate2025-10-19 — 2028-10-18

View original certificate image ↗
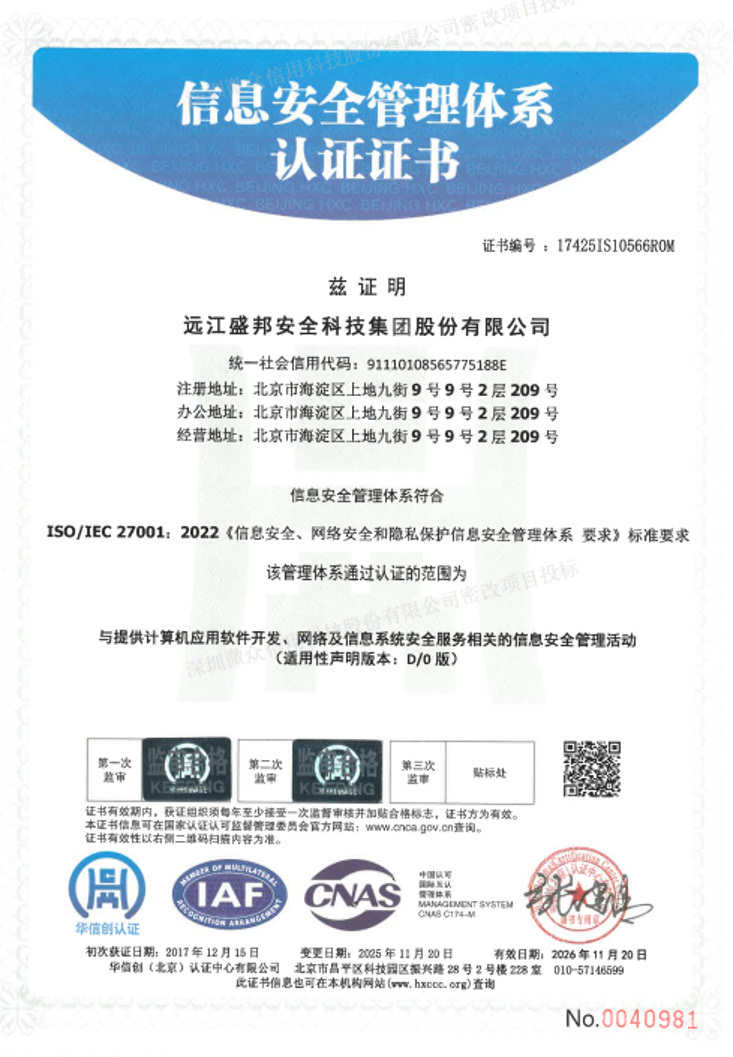
ISO/IEC 27001:2022 — 遠江盛邦安全科技集團股份有限公司

ISO/IEC 27001:2022

Information security management for the application software development, network and information-system security services specified in the certificate.

Validity stated on certificate2025-11-20 — 2026-11-20

View original certificate image ↗
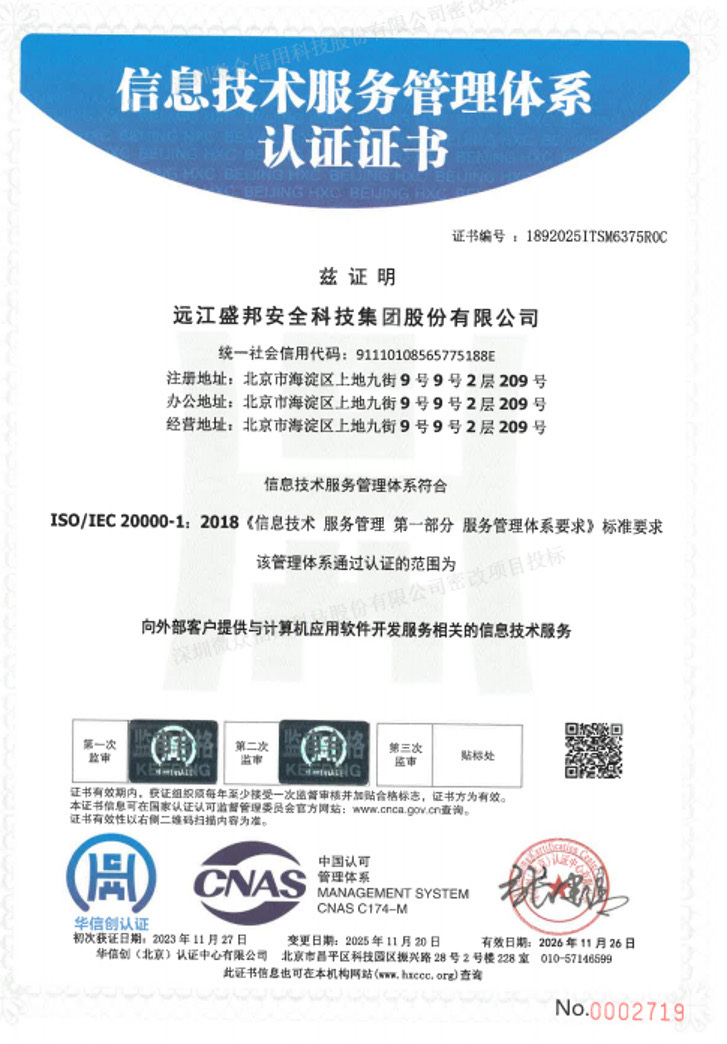
ISO/IEC 20000-1:2018 — 遠江盛邦安全科技集團股份有限公司

ISO/IEC 20000-1:2018

IT service management for application software development services provided to external customers within the stated scope.

Validity stated on certificate2025-11-20 — 2026-11-26

View original certificate image ↗

Reviewed on 2026-10-21. The attached ISO/IEC 27001 and ISO/IEC 20000-1 versions expire on 2026-11-20 and 2026-11-26 respectively. Request renewals and current status at procurement or project initiation. Certificates remain subject to the issuer’s surveillance and maintenance requirements.

Organisational credentials and individual project staff qualifications are reviewed separately. Vendor certificates are not presented as AL-Touch company certifications.

About WebRAY ↗


VENDOR RESOURCES · AL-TOUCH SELECTION NOTES

Technical resources and deployment essentials

Review features, deployment requirements and selection notes, then consult complete vendor documentation as needed.

Manufacturer white paper

2025 Cyberspace Mapping Technology White Paper

Inventory externally exposed assets, analyse exposure using discovery data and plan ongoing monitoring.

  • Combine active/passive discovery and public intelligence
  • Organise assets, services and network relationships
  • Use mapping results for exposure analysis and protection planning

Public PDF · July 2025

Read vendor resource
Product information

RayWAF: website and API protection

Compare web/API traffic inspection, business protection and deployment modes, then arrange policy testing and exception management.

  • Inspect web attacks and abnormal business requests
  • Identify APIs and inspect requests and responses
  • Choose proxy, inline or out-of-band deployment

Public product page

Read vendor resource
Product information

RayToken: enterprise AI access and data controls

Manage access, data transfer and usage records between business applications and AI models.

  • Allocate access by department, role and user
  • Inspect prompt injection and sensitive-data transfer
  • Audit model calls, usage and security events

Public product page

Read vendor resource
More vendor resources 2 items
Manufacturer white paper2025 Cyberspace Mapping Technology White PaperManufacturer 2025 white paper on mapping technology. Check current product pages for functionality.Technical documentationManufacturer RayWAF product introductionHistorical 2021 product PDF for architecture reference, not a current feature or licensing commitment.

Need to assess compatibility with existing systems?Discuss compatibility, deployment and licensing with the team.

Enquire about products and deployment

From product selection to deployment and maintenance

Describe your systems, scale and improvement needs to plan configurations, licences and deployment with the team.

Contact our Hong Kong team Local services and deployment →Browse other brands →