Protect websites and understand exposed assets.
AL-Touch provides WebRAY product consultation, deployment and Hong Kong support, connecting application protection, vulnerability management and ongoing monitoring.
Website and API protection
Configure application policies within RayWAF capabilities, tuning rules and exceptions to business traffic.
Vulnerability scanning and remediation
Arrange RayWVS/RayScan scope, testing windows and post-remediation verification.
Asset management and monitoring
Use RaySpace to organise public websites, subdomains and APIs, following up exposure and tampering risks.
Confirm licensing, deployment regions and local support during selection. List vendor credentials separately from AL-Touch's channel services.
View business cybersecurity servicesDeployment and handover
Product selection, deployment verification and handover
Match products and licences to usage, connecting purchasing, configuration, verification and daily management in a clear delivery scope.
Selection and licensing
Check users, devices, sites and key functions. Compare capacity, licensing and deployment conditions for the selected edition.
Deployment and integration
Confirm integration with existing networks, accounts and systems, then configure, migrate or pilot within the approved scope.
Verification and management
Test features and permissions in real workflows, clarifying responsibility for alerts, updates, renewals and support.
Confirm before purchasing
- Required features are included in the quoted edition and licence.
- Deployment prerequisites, third-party integrations and data handling are specified.
- Installation, training, updates and after-sales support are described separately.
Features, specifications, licensing, sales regions and availability depend on current vendor documentation and the formal quotation. New integrations or custom work require separate assessment.
On this page 10 sections
Network protection and vulnerability management: authorised WebRAY services
WebRAY focuses on integrated monitoring, defence and security governance. As an authorised Hong Kong channel partner, AL-Touch Solutions Hong Kong provides product sales, solution consultation, deployment and local technical support, bringing web protection and vulnerability management to businesses in Hong Kong and the Greater Bay Area.
Hong Kong channel agreement number: RAY-SME2025-HK-1. Confirm products, subscriptions, licensed territories and service scope against the selected solution and manufacturer documentation.
Manufacturer credentials and AL-Touch local support
The national-level credentials and major-event security experience described below belong to WebRAY, 遠江盛邦(北京)網絡安全科技股份有限公司, in mainland China. AL-Touch is its Hong Kong channel partner for sales, consultation and local support. This does not give AL-Touch those manufacturer credentials or the same major-event experience.
The manufacturer has supported major events including the Olympic Games and G20 Summit. Historical emergency-support credentials cover September 2021–August 2023 as a national-level cybersecurity emergency support organisation (CNCERT-2021-20230831GJ012), and January 2024–December 2025 at Grade A (CNCERT-2024-20251231JJ09). These records apply to the stated periods and do not establish that the same credentials remain valid in 2026.
Historical CNCERT lists: https://www.cert.org.cn/publish/main/32/9.html and https://www.cert.org.cn/publish/main/32/10.html.
RayWAF web application firewall
RayWAF provides application-layer protection for websites and business applications. Detection and blocking policies address SQL injection, cross-site scripting (XSS), web attacks and API security risks to help reduce the risk of business system compromise.
We tune rules to website and API traffic, review false-positive exceptions and assess effects on normal operations and high concurrency. Capacity, features and blocking performance depend on the model, licence, enabled policies and testing in the actual environment.
View full service informationExpand the remaining 7 sections for configurations, applications and service arrangements
RayWVS / RayScan vulnerability scanning and management
Vulnerability scanning identifies weaknesses in web applications, systems and business assets, providing remediation recommendations for risk-based follow-up. Management extends beyond a single scan to lifecycle tracking and verification after fixes.
Scans and reports for annual reviews, IT audits, VAPT or IPO preparation can be scoped to authorised assets. Agree permissions, test windows and potential business impact in advance.
RaySpace asset governance and continuous monitoring
Asset governance supports the digital asset lifecycle. Discovery and identification help catalogue exposed websites, hidden subdomains and APIs so businesses understand their network assets.
Monitoring also addresses website defacement and malicious-code insertion risks. Asset inventories and risk reports support annual reviews, remediation follow-up and security management across offices.
RayTRAP deception and manufacturer technology areas
RayTRAP uses simulation and honeypots to attract attackers and analyse behaviour for threat management. Confirm modules, licensing, detection data and deployment responsibilities for the specific solution.
WebRAY's portfolio also covers satellite internet security and encryption technology. Hong Kong projects require separate selection of applicable products, licences and local support.
Authorised supply and Hong Kong technical support
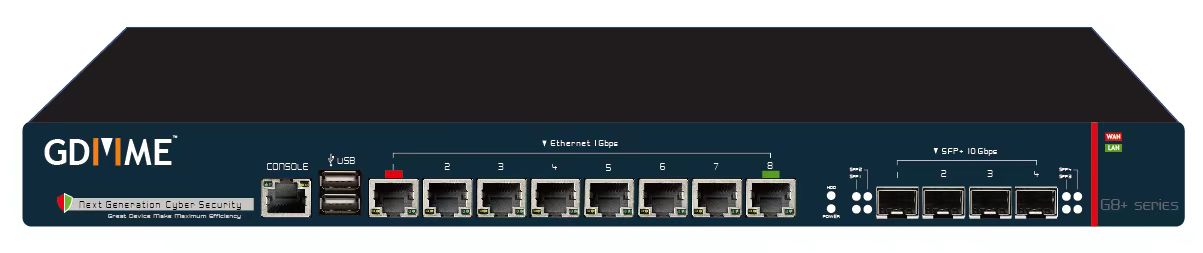
AL-Touch advises on and deploys WebRAY hardware, software and subscriptions. Product selection confirms manufacturer supply, warranty, technical support and signature-update arrangements, documented for procurement and ongoing maintenance.
Local services include equipment maintenance, spare-parts arrangements, onsite tuning, policy configuration and rule exceptions. Alerts can be handled with manufacturer support through the contracted incident coordination process. Onsite hours, replacement arrangements and response targets follow the agreed service scope.
Cross-border operations and data requirements
Businesses operating in mainland China, Hong Kong and Macau need to assess each jurisdiction's cybersecurity and data-processing requirements. WebRAY web protection, scanning and asset governance can support controls and review evidence across locations.
Applicability of graded protection, data security and other requirements depends on the institution, systems and actual activities. Deployment does not automatically satisfy every regulation or ensure a rapid audit pass.
Government, public-sector and infrastructure projects
Government, public-sector and airport-related procurement commonly calls for assessment of system stability, application security, vulnerability management and maintenance. RayWAF and RayScan can form part of a technical proposal with risk assessment and acceptance testing.
We organise applicable product, testing and handover information against procurement documents from organisations such as AAHK. Individual projects still require their own technical assessment and acceptance.
Defacement protection for financial and e-commerce applications
Corporate websites, financial applications and e-commerce platforms facing SQL injection, XSS or defacement risks can combine WAF, signature updates, remediation and monitoring to help protect customer information and transaction systems.
Multinational businesses can plan policy management across Hong Kong, mainland China and other offices, while reviewing data flows, third-party support and evidence for each system's controls.
Information and references
Suitability and enquiry preparation
When is this service suitable?
Common needs
- A public website or store needs a security-risk review.
- Applications use plug-ins, APIs or external integrations, and protection scope needs clarification.
- Discovered vulnerabilities or anomalies require clear testing, patching and maintenance responsibilities.
Which service do I need?
- WebRAY application security
Discuss website, API and vulnerability assessment scope.
- Business website design
Clarify redesign and routine update responsibilities together.
- Business cybersecurity
Review protection of related systems and data.
Prepare for an enquiry
- Describe the application and public entry points; do not provide administrator passwords.
- Current development, maintenance and hosting responsibilities.
- Assessment scope, main concerns and preferred timing.
For an initial enquiry, describe the issue and equipment only. Do not submit passwords or verification codes. The team will arrange a secure channel for sensitive documents and incident records.
Enquire about website and application securityCybersecurity and AI useExplore security planning, responsibilities and acceptance considerations
Cybersecurity · Safe AI use
Web and business application security: security planning priorities
「WebRAY cybersecurity」 includes the following security priorities; measures, tests and deliverables are specified in the proposal.
- Application scopeInventory websites, APIs, administration interfaces and data flows, defining protection and vulnerability-assessment scope around actual usage.
- Configuration and testingCheck policies, updates and testing against selected products and licences, assessing business impact and exceptions.
- Remediation and maintenanceSeparate responsibilities for discovery, remediation, retesting and daily alerts. Deploying a security product does not mean every issue is resolved.
AI considerationsFor AI chat, knowledge bases or tool calls, separately review data access, public input and tool permissions. Explicitly include AI tests and controls in project scope.
Planning and acceptance recordsApplication and API scope, policy and test records, remediation/retest and maintenance responsibilities.
You may also want to know
For one business website, should we enquire about scanning or protection first?
List the website, administration interfaces, APIs and known problems. Scanning helps identify weaknesses and organise fixes; protection addresses application traffic risks. Prioritise products and deployment around the importance of each asset.
Are RayWAF and vulnerability scanning the same service?
RayWAF focuses on application traffic protection. RayWVS / RayScan identify vulnerabilities and support remediation follow-up. Select a combination based on assets, traffic and risks.
Are the manufacturer's national-level credentials AL-Touch credentials?
No. Manufacturer history and major-event experience are separate from AL-Touch's Hong Kong channel relationship and local support. Dates and the scope of each record must remain explicit.