From office networking to layered business protection.
GDMME combines network engineering and security deployment to plan firewalls, segmentation and VPNs for Hong Kong offices, branches and cross-border businesses.
Boundaries and segmentation
Configure firewalls, IDS/IPS and VLANs around applications and sites, managing incoming, outgoing and internal traffic.
Endpoints and intelligence
Combine Huorong Enterprise, Zenarmor and CrowdSec where appropriate, planning endpoint and network controls together.
Deployment and managed services
From equipment selection and physical connections to rules and maintenance, arrange testing and daily management.
Confirm modules, licences, capacity and support by model and plan, then test in the actual environment.
Explore GDMME MFS managed servicesDeployment and handover
Product selection, deployment verification and handover
Match products and licences to usage, connecting purchasing, configuration, verification and daily management in a clear delivery scope.
Selection and licensing
Check users, devices, sites and key functions. Compare capacity, licensing and deployment conditions for the selected edition.
Deployment and integration
Confirm integration with existing networks, accounts and systems, then configure, migrate or pilot within the approved scope.
Verification and management
Test features and permissions in real workflows, clarifying responsibility for alerts, updates, renewals and support.
Confirm before purchasing
- Required features are included in the quoted edition and licence.
- Deployment prerequisites, third-party integrations and data handling are specified.
- Installation, training, updates and after-sales support are described separately.
Features, specifications, licensing, sales regions and availability depend on current vendor documentation and the formal quotation. New integrations or custom work require separate assessment.
On this page 21 sections
Next-generation network security for Hong Kong businesses
GDMME® combines traffic management, alerts and layered protection for Hong Kong offices, cross-border factories, remote work and branch connectivity. Consumer or entry-level equipment may not cover cross-border access, lateral movement and business administration requirements.
AL-Touch provides technical deployment and local support. GDMME can work alongside Huorong Enterprise for endpoint and network protection. Financial and other sector requirements still need assessment against institutional status, activities and actual control evidence.
AI security engine and Intel hardware platform
GDMME next-generation firewalls combine a HardenedBSD security core, the Zenarmor® AI security engine and optional CrowdSec global threat intelligence. G6 / G6+, G8 and G12 solutions offer different configurations; selection depends on hardware, software versions and required modules.
Intel processors, systems-on-chip and Ethernet controllers form the hardware platform for PCIe connectivity, packet processing and encryption. Network adapter, DPDK and hardware-acceleration support and activation depend on the model and deployment.
AL-Touch's Intel Partner Alliance and joint-development relationship describes hardware integration and technical development. It does not constitute an express or implied legal warranty by Intel for a particular GDMME product.
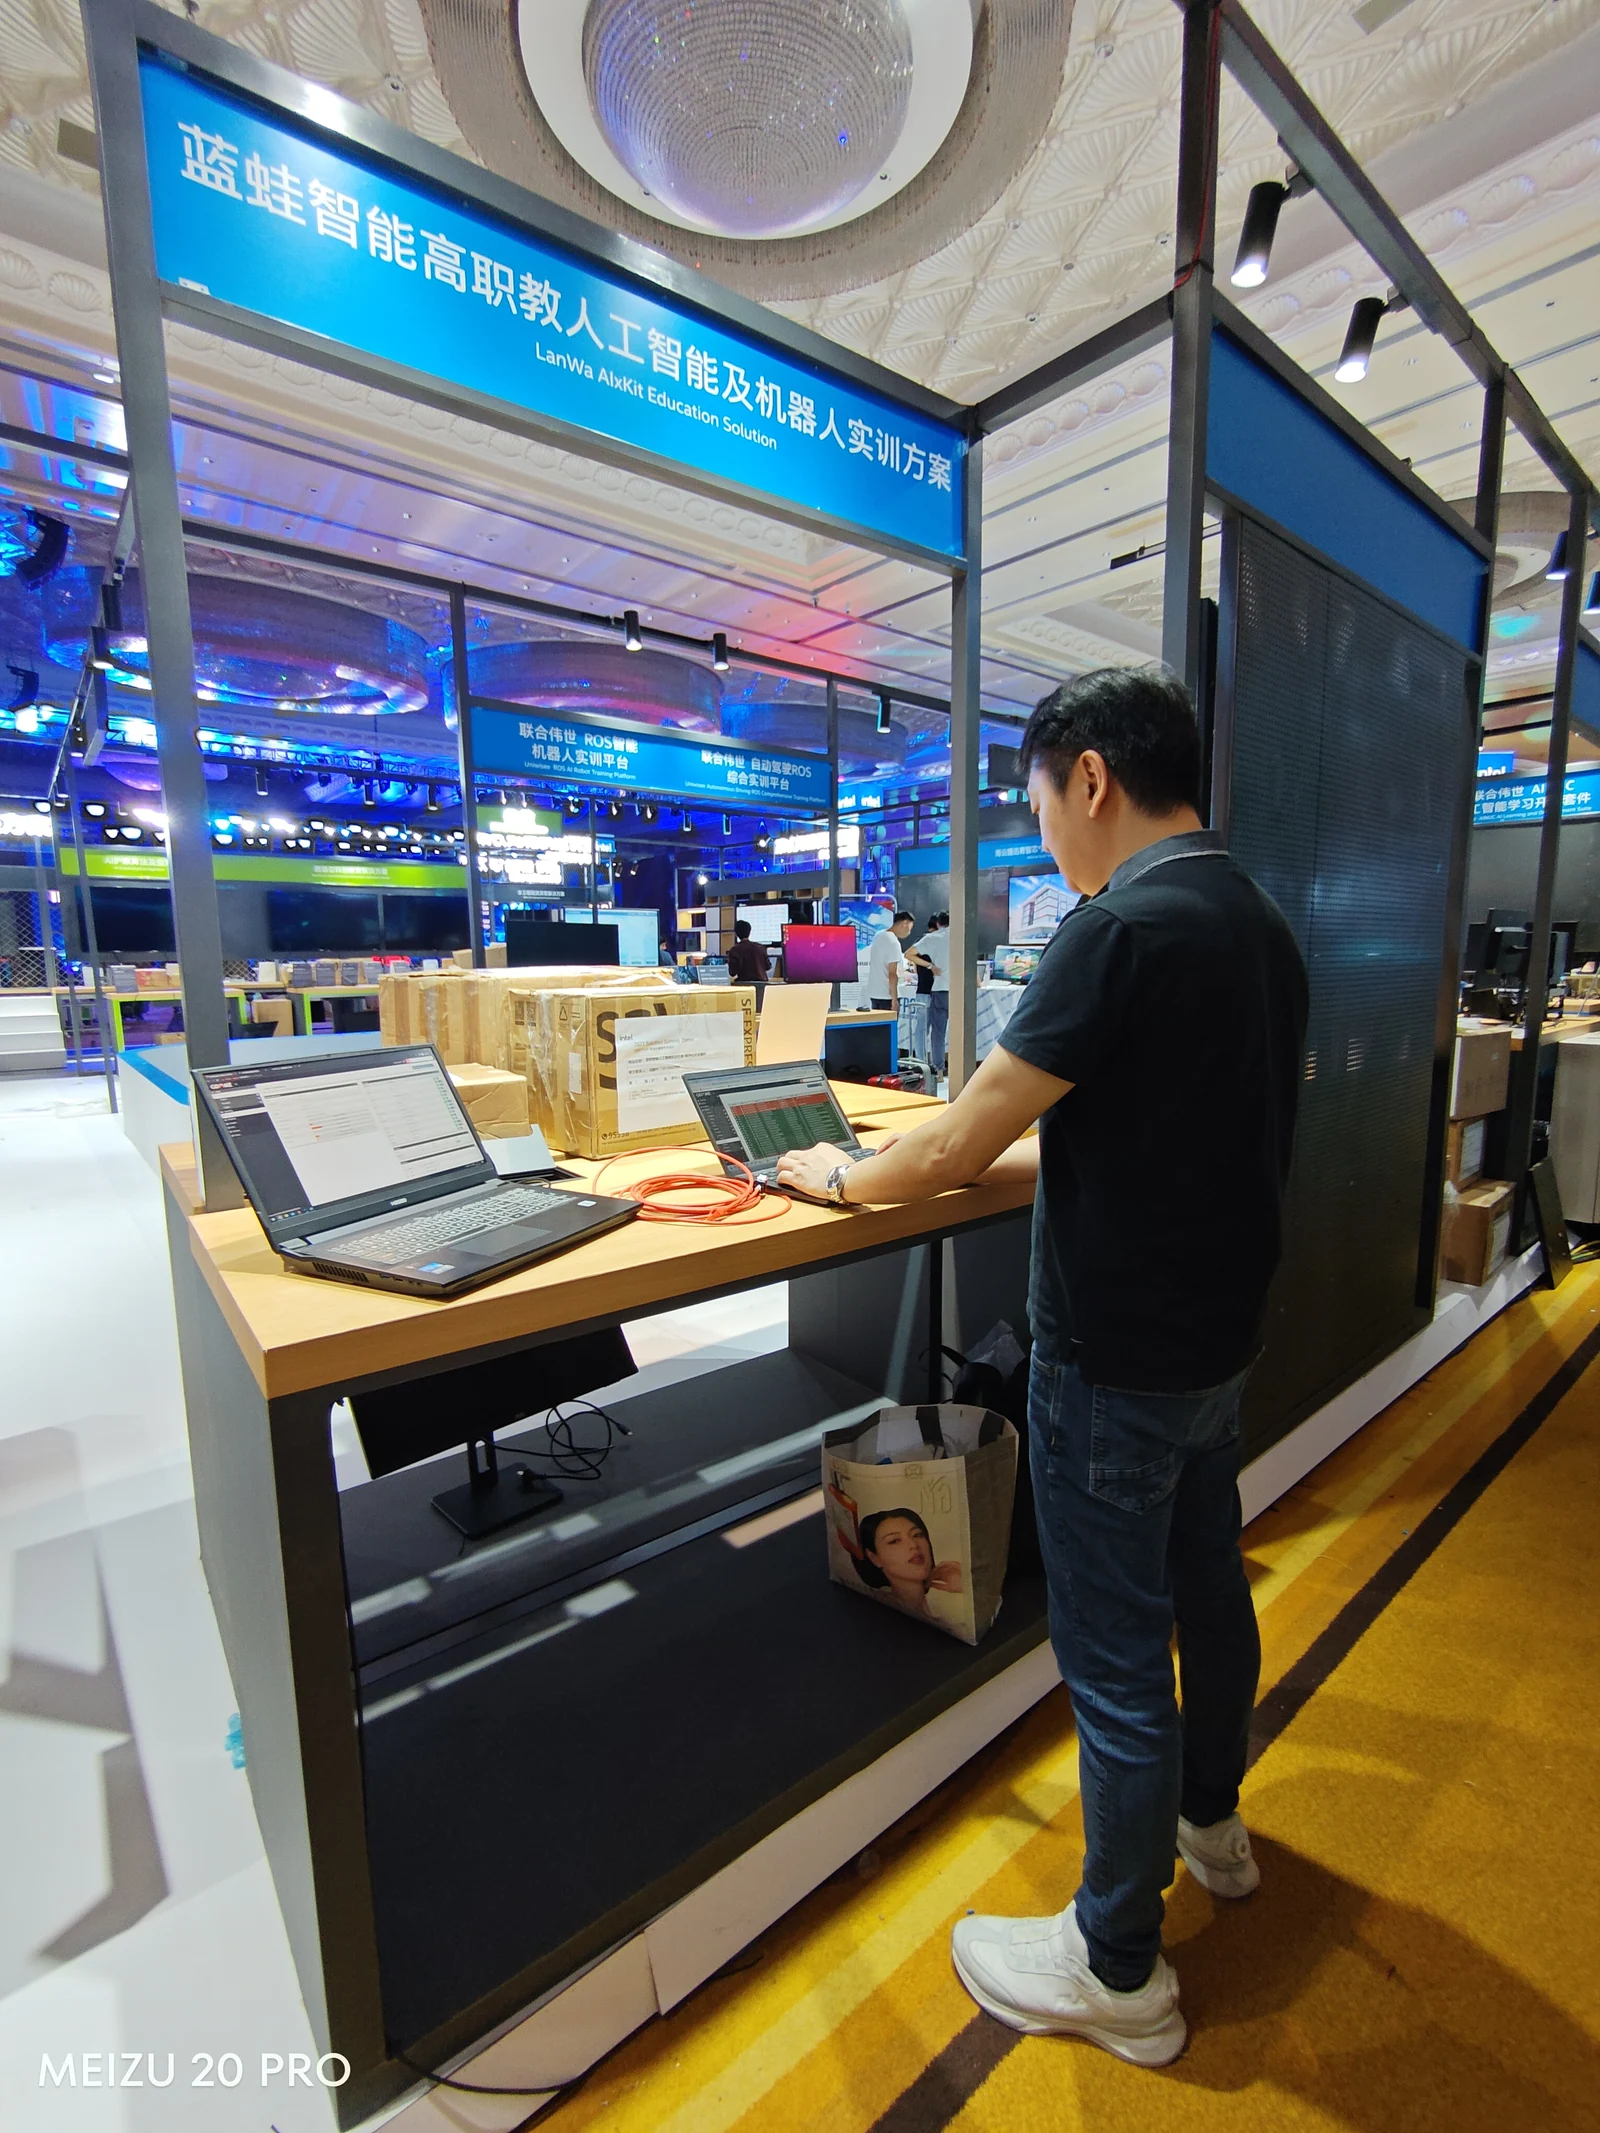
Deployment experience: networking and security at a solutions summit
GDMME G6 uses an Intel commercial platform, with processing capacity planned around onsite endpoints, traffic and security policies.
Deployment photographs show GDMME G6 operating at the edge of a real commercial event, supporting core network security monitoring and connectivity at a solutions summit.
As the summit's networking contractor, we deployed a GDMME® G6 next-generation firewall to support core network security and traffic across the venue.
AL-Touch installed the wired and wireless networks, with GDMME G6 as the core traffic gateway. NAS and AI workstations requiring stable connections used wired access; attendees and mobile devices used Wi-Fi.
The event supported over 300 wired and wireless endpoints with mixed workloads including AI applications and global 4K live streaming. These figures describe that event's configuration and workload; other projects require assessment against their hardware, policies and environment.
View full service informationExpand the remaining 18 sections for configurations, applications and service arrangements
Summit engineering: mixed traffic, isolation and two-day operation
The summit network carried commercial and education demonstrations, AI development, gaming broadcasts, cloud rendering and autonomous-driving demonstrations. Engineers integrated and tuned GDMME G6, Intel x64 and H3C Wi-Fi for access, traffic management and isolation.
Equipment ran continuously for 48 hours during the two-day event, supporting global streaming and concurrent demonstrations. Auto M-Gate-Deployer and customised policies helped configure isolation and traffic mapping within the limited setup window.
Onsite photographs and case information illustrate AL-Touch's networking and deployment experience. For business projects, we adjust hardware and policies to endpoint numbers, operating requirements and workloads such as streaming, then test performance and latency to plan capacity.
GDMME NGFW models, interfaces and multi-WAN configuration
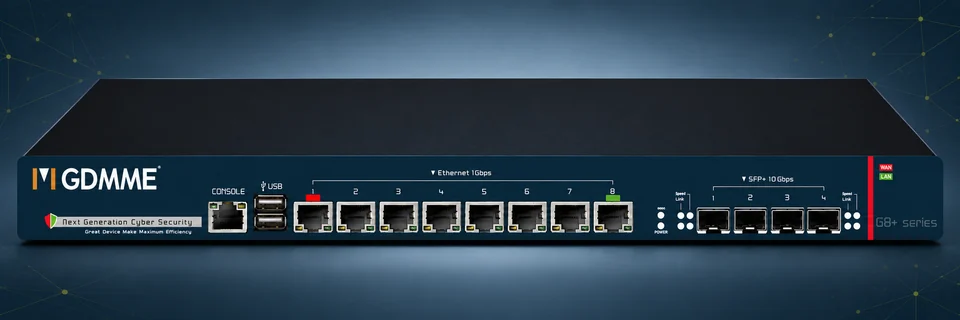
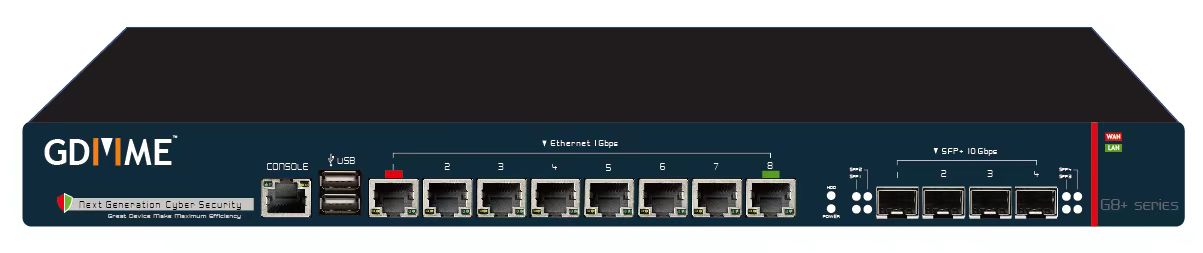
G6 / G8 options include Intel x86 / x64 architecture, console, USB 3.0, 2.5G copper ports, SFP+ 10G fibre interfaces and optional redundant power. Available combinations extend to eight 2.5G copper ports and four 10G interfaces. Confirm each model's ports and power configuration in the quotation.
G6 offers configurations with up to seven WAN connections. Aviation, maritime and historical D-Biz projects used different ports, WAN counts and throughput configurations. Validate multi-WAN, HA, VPN and performance with IDS/IPS and other modules enabled for the specific configuration.
Automated gateway deployment and preconfiguration
GDMME (Great Device, Maximum Management & Efficiency) uses Auto M-Gate-Deployer automation to simplify firewall configuration and routine maintenance, supporting factory preconfiguration, DHCP connectivity and static IP settings.
Factory settings can include IDS/IPS and DNS protection rules; Zenarmor's AI engine is an optional subscription. Zero-touch deployment can be planned around preset configurations and network conditions. Routing, licences, policies, remote access and testing still need review before launch; five-minute deployment is not guaranteed for every environment.
Layer one: GDMME hardware NGFW perimeter protection
Configure firewalls, IDS/IPS, segmentation and traffic controls at the internet boundary to help reduce risks from malicious sources, unauthorised intrusion and known threats. DDoS protection also depends on upstream connectivity and other protective arrangements.
Layer two: Workstation VM-NGFW virtual firewall
A lightweight firewall in the workstation's virtual layer filters inbound and outbound traffic according to policy. It aims to strengthen individual-device isolation and reduce data leakage or lateral movement after operating-system compromise. Confirm platform compatibility, performance and management arrangements before deployment.
Layer three: OS hardening and Huorong endpoint management
Windows Firewall and HUORONG Enterprise Endpoint Security Management System V2.0 support OS hardening, process and port policies, abnormal-behaviour monitoring and unauthorised-access controls, complementing perimeter protection.
HardenedBSD mechanisms such as ASLR, W^X and SafeStack mitigate exploitation; Zenarmor and CrowdSec provide detection and intelligence at different layers. Integration can reduce some attack paths, but does not make zero-day exploitation impossible or automatically satisfy all Hong Kong and mainland regulations.
Protected traffic paths: workstation, DNS, application and perimeter
We coordinate workstation VM-NGFW, GDMME appliances and perimeter controls along managed traffic paths so each module addresses its relevant risks.
- Workstation: confirm application network permissions and device-isolation policies.
- DNS: apply blocklists and encrypted DoH queries according to policy; malicious domains can be blocked during resolution.
- Application: Zenarmor identifies Layer 7 applications and web categories; IDS/IPS inspects packets against rules.
- Perimeter: CrowdSec Bouncers block high-risk IPs using intelligence, while Agents contribute behavioural monitoring. Confirm intelligence uploads, data flows and subscription scope during deployment.
Three technical pillars: deployment, isolation and the security stack
Customised deployment automation combines factory rules, network settings and remote management. Hardware-isolation designs use PCIe, WAN and virtual/host responsibilities to define controlled traffic paths. Validate the actual architecture; this is not a physically disconnected air gap.
IDS/IPS, DNS controls, Zenarmor and CrowdSec offer complementary protection. Optional CrowdSec Premium and frequent intelligence synchronisation depend on the selected version and subscription, including update frequency, coverage and data exchange.
Nine business cybersecurity threats
- Ransomware: encrypts or steals business information for extortion, affecting availability, confidentiality and recovery.
- Phishing: disguised emails, messages or websites persuade staff to disclose credentials or execute malicious content.
- Data breaches: unauthorised access, sharing or publication of customer or business information affects privacy, reputation and operations.
- Insider threats: mistakes, excessive permissions or malicious activity can cause data leakage or system damage.
- Zero-day vulnerabilities: attacks exploit flaws without an available patch, requiring access restrictions, monitoring and mitigation.
- DDoS: large volumes or targeted requests consume network and system resources, disrupting websites or online services.
- Mobile-device security: inadequate BYOD updates, account controls or data management increase intrusion and leakage risks.
- Remote-desktop risks: exposed entry points, weak passwords or excessive permissions can enable access to business networks.
- Cloud threats: misconfiguration, oversharing or inadequate authentication expose data and services.
Zenarmor's manufacturer ecosystem and international applications
Zenarmor, formerly Sensei, is a next-generation firewall software engine for application identification, threat intelligence and network security management. Confirm capabilities such as BrightCloud intelligence in Business Edition against the manufacturer's version and subscription.
Manufacturer cases include Nebulex financial services, network provider 5th Mountain, Fred Loya Insurance, Innovation Federal Credit Union, Norway's WebMed EPJ AS and the Netherlands' De Hooge Waerder. These are Zenarmor cases, presented separately from AL-Touch's local delivery.
Applications include data-centre perimeter protection, application control, SASE and branch policies, and adding inspection to existing networks. Manufacturer experience can inform selection; GDMME protection and management outcomes require validation for the chosen configuration.
Hong Kong aviation: NGFW deployment across borders
Hong Kong and cross-border aviation operations require stable networking, encrypted inter-region VPNs and strong perimeter controls.
The aviation solution focuses on encrypted VPNs, HA, IDS/IPS, anti-malware and long-term maintenance. The case used a 1Gbps configuration with basic firewall and IDS enabled. Test throughput and failover against equipment, modules and load.
Hardware: a flagship 2U gateway with an enterprise multicore processor, two 10Gbps fibre interfaces and six gigabit copper ports.
Security functions: IDS/IPS, anti-malware, web filtering, GeoIP blocking, two-factor authentication, DNS protection and encrypted inter-region VPN tunnels.
Service options include managed security rental, manufacturer hardware maintenance, intelligence updates and upgrades across years. Specify 24/7 HA operation separately from staffed coverage and response targets.
Aviation deployment cases from 2019
Cross-border business aviation company, from 2019: deployed a flagship gateway as a core network defence and completed group technical review and acceptance.
Hong Kong–mainland business aviation group, 2019: delivered GDMME firewalls aligned with cross-border access and security processes, with threat protection scoped to the project.
Macau international aviation organisation, 2019: deployed GDMME NGFW, security gateways and VPN Server access.
The solution aims to improve availability, support expansion and reduce upfront costs through rental. Network and account controls can support privacy and business requirements; deployment alone does not establish full compliance with privacy law or industry standards.
Hong Kong maritime engineering: international shipping NGFW
Maritime engineering groups, ocean-going fleets and terminals need long-term connectivity through overseas VPNs, headquarters–vessel–port links, multi-WAN, HA and segmentation.
The maritime solution uses GDMME G6 1U, firewall and IDS, up to five-WAN load balancing and HA clustering, with GeoIP, DNS blocklists and QoS shaping. The 1Gbps figure and failover targets apply only to the corresponding tests and configuration.
Options include hardware delivery, monthly managed services or annual maintenance with local engineers. Confirm the geographical coverage, hours and targets of the emergency four-hour onsite service option in urban Hong Kong through the contract.
Maritime engineering cases from 2021
Case 1 | International ship-management group, from 2021: deployed a two-node hot-standby HA cluster, with recorded stable operation over several years and completion of cross-national project closeout.
Case 2 | Fleet company headquarters, from 2021: installed a rack-mounted 1U firewall in a maritime engineering office, with recorded stable year-round operation.
Hot standby, multi-WAN and link failover support availability; segmentation, anti-malware and access control reduce ransomware and cross-border leakage risks. Confirm historical operating records separately from current maintenance and service scope.
D-Biz Category 11: historical cybersecurity projects
As a supplier for Category 11 cybersecurity solutions under the former D-Biz programme, AL-Touch provided local installation, acceptance documentation and follow-up. The following are historical 2021 projects, not current funding-application information or government compliance certification for every product.
Those projects used 1U, six-port and multi-WAN configurations, with IDS/IPS, anti-malware, web filtering, GeoIP, two-factor authentication and VLAN isolation. Hardware and documents followed the requirements of those projects.
Case 1 | Business consultancy, 2021: received D-Biz funding, deployed GDMME NGFW and completed government acceptance.
Case 2 | Heavy-industry infrastructure contractor, 2021: deployed a firewall at a large site to separate internal and external networks and completed D-Biz review.
Case 3 | Supply-chain trading business, 2021: deployed GDMME G6 1U with support for the funding application process and acceptance.
These cases demonstrate historical planning, installation and documentation experience. Individual approvals and acceptance records do not guarantee outcomes for other organisations, years or current funding programmes.
Cross-border manufacturing: branch VPNs and isolation
Manufacturers operating across Hong Kong and mainland China need encrypted headquarters–factory connections, internal segmentation, WAN backup, QoS and long-term maintenance for multiple sites, staff and higher traffic volumes.
The solution uses GDMME G6 1U with optional dual 10Gbps fibre, HA, IPsec VPN, VLAN, DNS blocklists and GeoIP. Validate a 1Gbps configuration against enabled modules and actual load.
One-off delivery or monthly managed services can include Hong Kong remote monitoring, monthly onsite computer health checks and equipment cleaning. Specify coverage, equipment, staffing and targets for urban Hong Kong emergency four-hour attendance or Hong Kong/mainland teams in the contract.
Cross-border manufacturing cases from 2021 and 2022
Hong Kong–mainland manufacturing group, from 2021: deployed GDMME firewalls in phases across the Hong Kong headquarters and mainland factories, establishing cross-border VPNs and access management.
Cross-border manufacturing site, from 2022: deployed GDMME firewalls and enterprise Wi-Fi 6 access points for site coverage, monthly managed services and monthly onsite maintenance.
The solution supports inter-factory networking, staff internet policies and segmentation to reduce disruption and data risks. Link quality, availability and protection still require assessment against the environment and maintenance records.
Hong Kong integration, collaboration and service scope
AL-Touch offers hardware delivery, monthly managed services, onsite maintenance and incident support. Cooperation with 華白科技 combines network contracting experience with GDMME, Zenarmor and CrowdSec configuration, from physical cabling to perimeter protection.
24/7 remote SOC or monitoring and emergency response are configurable services. Confirm staffing, alert sources, response and attendance targets in the service contract, separately from product licences.
Team members' CCSS-R credentials are historical individual qualifications under the 2021–2024 former system. HKPC, AAHK and other procurement relationships are listed separately from product functionality, corporate compliance and project delivery.
GDMME's reference to Unix architecture describes the Unix-like HardenedBSD security core; it does not imply a UNIX trademark licence from The Open Group. Confirm hardware specifications, intelligence updates, performance and protection through configuration, policy and environmental testing.
Information and references
Suitability and enquiry preparation
When is this service suitable?
Common needs
- The company lacks clear network boundaries or device access arrangements.
- Firewall replacement is an opportunity to review policies and management responsibilities.
- More offices, branches or remote users require deployment assessment.
Which service do I need?
- GDMME cybersecurity solutions
Explore network defence and deployment scenarios.
- MFS managed firewall
Discuss daily management, alerts and response responsibilities.
- Enterprise endpoint security
Explore protection management for employee computers.
- Business data backup
Include recovery from data incidents in the discussion.
Prepare for an enquiry
- Company size, office locations and main system types.
- Existing security tools and management responsibilities.
- Main concerns, affected areas and target improvement timeframe.
For an initial enquiry, describe the issue and equipment only. Do not submit passwords or verification codes. The team will arrange a secure channel for sensitive documents and incident records.
Enquire about GDMME networkingCybersecurity and AI useExplore security planning, responsibilities and acceptance considerations
Cybersecurity · Safe AI use
Business cybersecurity and managed protection: security planning priorities
「GDMME: Next-Gen Edge Security & Managed Firewall Solution」 includes the following security priorities; measures, tests and deliverables are specified in the proposal.
- Assets and defencesIdentify systems, endpoints and networks to protect, checking applicable products, modules and policies for each scenario.
- Data and monitoringClarify log, intelligence and alert sources, exchanged data and recipients, defining monitoring and handling activities covered by the service.
- Response and responsibilitiesDiscuss incident classification, policy changes, recovery and business/support responsibilities, documenting owners and procedures for each task.
AI considerationsInventory AI assistant or agent data, service accounts and tool permissions separately. Network or endpoint protection does not cover every prompt-injection or agent-action risk.
Planning and acceptance recordsAsset and control lists, policy and alert-test records, incident procedures and service responsibilities.
You may also want to know
Can a small office keep existing equipment and improve protection gradually?
Provide routers, firewalls, links, user numbers and connected systems. The team can compare reusable equipment with additional GDMME configurations and arrange tests for traffic, VPNs, segmentation and required modules.
Does buying GDMME include every module and 24/7 staffed service?
Confirm the model, software licences, Zenarmor / CrowdSec subscriptions and managed-service contract separately. HA equipment operation is not the same as purchasing staffed coverage or incident response.
Do the summit and industry-case capacities apply to every deployment?
No. The 300 endpoints, 48 hours, 1Gbps and WAN/interface configurations describe particular projects or configurations. Actual performance depends on hardware, policies, modules and environmental testing.
Do D-Biz cases mean the same funding is still available?
They record historical delivery and acceptance, not currently available funding. New projects must confirm the programmes and conditions applicable at the time.