










Hong Kong business · Product selection and integration

CrowdSecProducts and features

Analyse local logs and collaborative intelligence, protecting servers, websites and network equipment through compatible remediation components.

Manufacturer information reviewed: 2026-10-13

GDMME technical integration

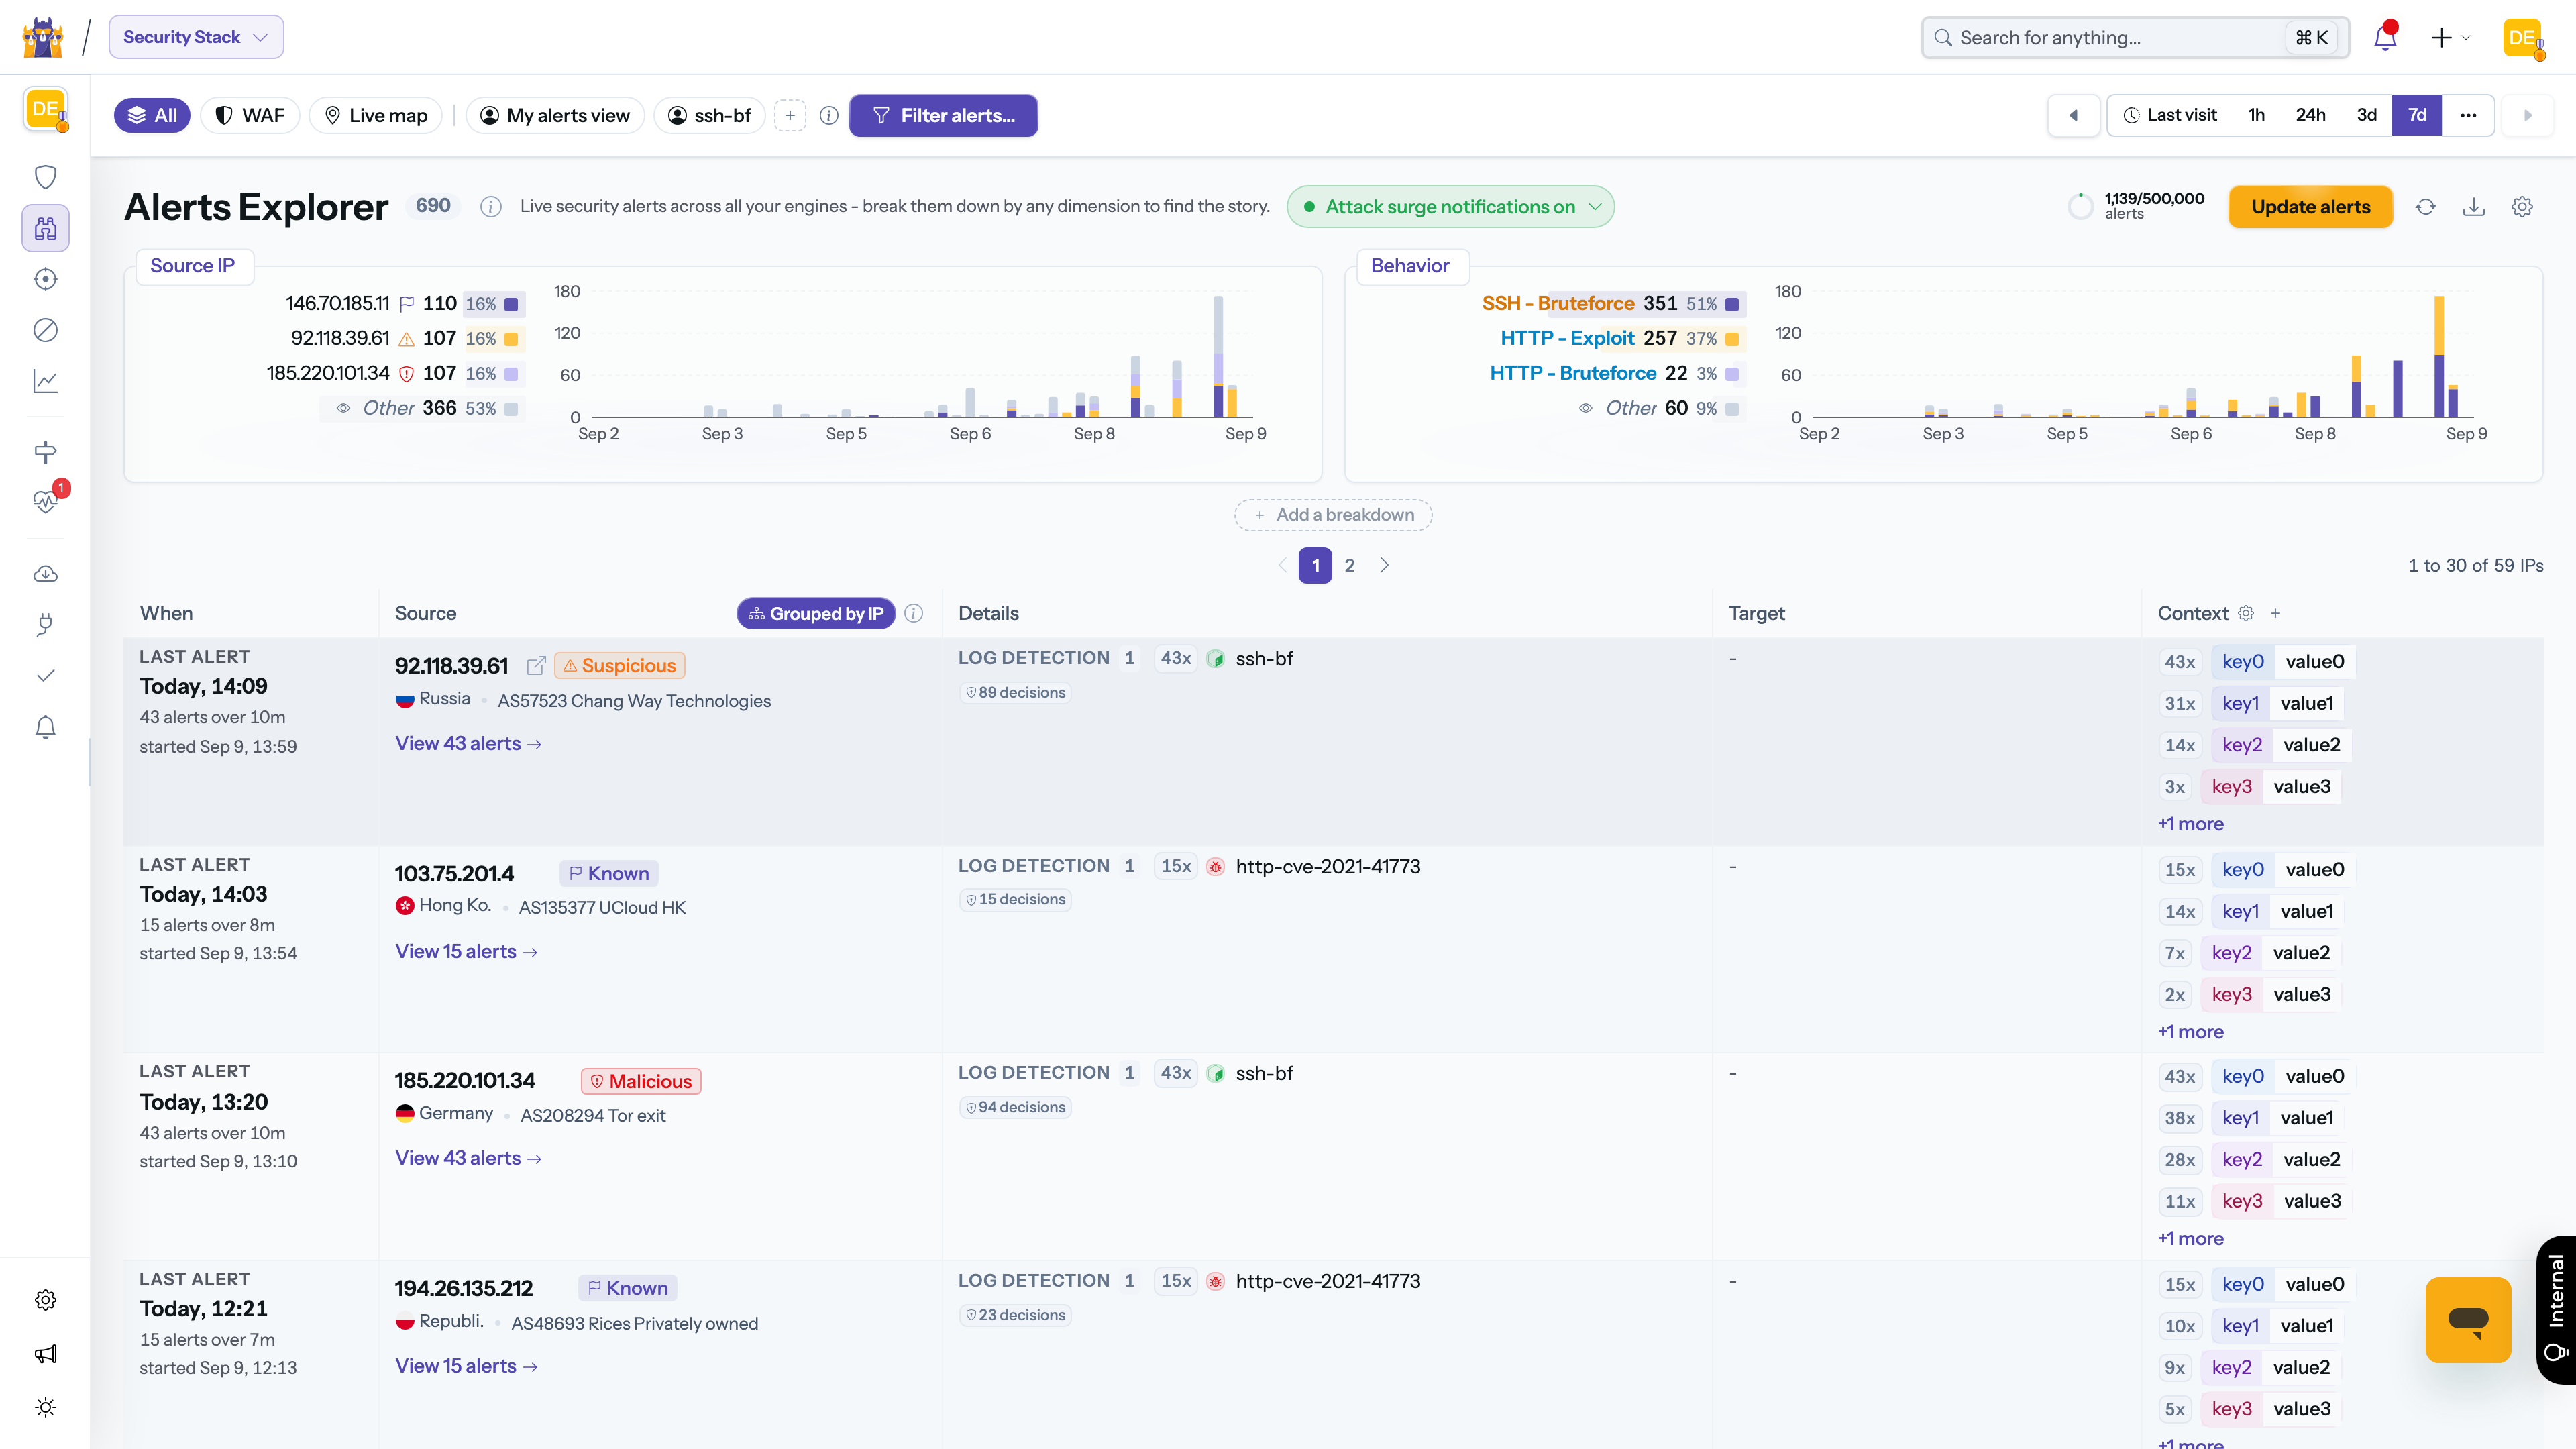
Official CrowdSec Alert Explorer showing alert trends, source-IP groups and events
Vendor Alert Explorer interface example, with sample data from official documentation.Vendor image source
5Product and feature categories
4Manufacturer resources
Manufacturer documents and technical information

PRODUCTS & CAPABILITIES

Product capabilities and environments

Covers behaviour detection, web protection, IP intelligence and central management. AL-Touch provides GDMME integration; confirm components, subscriptions and licences for each deployment.

Security Engine | Behaviour detection

Parse local logs and produce actionable decisions from attack scenarios.

  • Identify attacks from local logs
  • Generate remediation decisions from scenarios
  • Enforce decisions through compatible remediation components

Suitable scenariosServers, websites and containers

Key capabilities and scope
  • Manage log sources, parsers and scenarios
  • Detect brute force, scanning and other attack behaviour
  • Provide decisions to remediation components through the Local API
  • Optional participation in collaborative intelligence

Suitable environments
Servers · Web services · Containers and cloud environments

Configure log sources, detection rules and compatible remediation together. Security Engine performs detection and produces decisions.

Enquire about product solutions

AppSec | Web application protection

Inspect HTTP requests on supported web servers or reverse proxies.

  • Inspect web requests against attack rules
  • Combine virtual patching and behaviour detection
  • Integrate compatible servers and reverse proxies

Suitable scenariosWebsites and public web applications

Key capabilities and scope
  • Virtual patching and WAF rules
  • ModSecurity-compatible rules
  • Request inspection linked with behaviour detection
  • Integrations including Nginx, Traefik and HAProxy

Suitable environments
Websites · Reverse proxies · Public web applications

Enable an AppSec data source and compatible request-forwarding component, then test rules. IP blocking and HTTP inspection are different protection layers.

Enquire about product solutions

Blocklists | Malicious-IP intelligence

Deliver curated IP intelligence to compatible firewalls, CDNs or WAFs.

  • Subscribe to curated malicious-IP intelligence
  • Integrate engines or compatible devices
  • View list updates and subscription status

Suitable scenariosFirewalls, gateways, CDNs and WAFs

Key capabilities and scope
  • Community and subscription intelligence lists
  • Works with Security Engine or direct device integrations
  • Manage subscriptions, quotas and update status in the console

Suitable environments
Firewalls · CDN · Gateways and WAF

Confirm intelligence sources, update frequency and quotas for the subscription. Maintain allowlists and business exceptions; intelligence coverage has limits.

Enquire about product solutions

CTI | IP reputation and incident investigation

Review IP behaviour, attack history and timelines to assess alerts and investigate incidents.

  • Review IP behaviour and attack history
  • Search threat intelligence using incident indicators
  • Connect investigation tools through APIs

Suitable scenariosSecurity investigation and SIEM/SOAR

Key capabilities and scope
  • Investigate IP addresses through the web interface
  • CTI API integration with SIEM and SOAR
  • Search by behaviour, CVE, country and AS
  • Attack history and recent exploitation indicators

Suitable environments
SOC investigations · SIEM/SOAR · Internal security tools

API and web query quotas are counted separately and depend on the plan. Intelligence queries do not replace evidence from your own environment.

Enquire about product solutions

Console | Central visibility and management

View alerts, remediation status and operational health across multiple engines.

  • View alerts across multiple engines centrally
  • Track remediation metrics and deployment health
  • Enable advanced management by subscription

Suitable scenariosMultiple servers and distributed security deployments

Key capabilities and scope
  • A central view of multiple Security Engines
  • Alert analysis and remediation metrics
  • Manage lists and deployment health
  • Optional Premium notifications, decision synchronisation and predictive lists

Suitable environments
Multiple-server environments · Security teams · Distributed deployments

Confirm Premium features and subscription details with the vendor. Console records and data sharing must follow the organisation's data-handling policies.

Enquire about product solutions

VENDOR RESOURCES · AL-TOUCH SELECTION NOTES

Technical resources and deployment essentials

Review features, deployment requirements and selection notes, then consult complete vendor documentation as needed.

Technical documentation

Security Engine architecture and introduction

Distinguish log analysis, attack detection and enforcement, checking required components and connections.

  • Parsed logs and scenario rules produce decisions
  • Corresponding remediation components enforce blocking
  • Verify detection and enforcement after installation

Publicly readable

Read vendor resource
Technical documentation

AppSec web-protection integration guide

Send website or reverse-proxy requests to AppSec, planning real-time blocking and background analysis separately.

  • Select a compatible forwarding component for the platform
  • Separate real-time and background rule processing
  • Manage rules and alerts centrally

Publicly readable

Read vendor resource
Technical documentation

IP intelligence and alert-investigation guide

Assess alerts using IP behaviour, timing and attack context, choosing web queries or API integration.

  • Interpret IP intelligence through behaviour and time context
  • Enrich SIEM alerts through APIs
  • Check separate query and integration quotas

Publicly readable

Read vendor resource
More vendor resources 4 items
Technical documentationSecurity Engine getting-started guideHow logs, scenarios, decisions and remediation components work together.Technical documentationAppSec / WAF configuration documentationRequest inspection, web server integration and deployment requirements.Technical documentationBlocklists integration documentationList subscriptions, Security Engine and direct device integration.Technical documentationCTI API and investigation guideQueries, quotas, APIs and security tool integration.

Need to assess compatibility with existing systems?Discuss compatibility, deployment and licensing with the team.

Enquire about products and deployment

From product selection to deployment and maintenance

Describe your systems, scale and improvement needs to plan configurations, licences and deployment with the team.

Contact our Hong Kong team Local services and deployment →Browse other brands →